🏠 Home
Cybersecurity
🔐
Cybersecurity
1 channels · 162 articles
Articles
Prediction Markets Emerge as a New Vertical for Traffer Teams
Executive Summary
Since the spring of 2026, Insikt Group has observed multiple Russian-language traffer teams that have quickly adapted affiliate-fraud models to capitalize on growing public interest in prediction markets such as PolyMarket and Kalshi. The platforms offered by three such teams — AtlasCore, PolyFucked, and Magnetic Team — provide websites, administrative panels, cryptocurrency payment infrastructure, victim-management capabilities, technical support, and promotional guida
0
7
Behind Japan’s Warnings of a Cyber Crisis
Reporting on cyberattacks against Japanese entities rose 48% between Q2 and Q3 2026, encompassing ransomware, exploitation of vulnerabilities, credential leaks, and service disruptions. Significant incidents exposed millions of customer records and disrupted operations across multiple sectors, with attacks on shared service providers extending the impact to downstream organizations. Further incidents in October 2026 indicate that these trends have persisted into Q4. This report examines potentia
0
10
PHP2Shell Exploitation: Two Critical PHP Flaws Explained
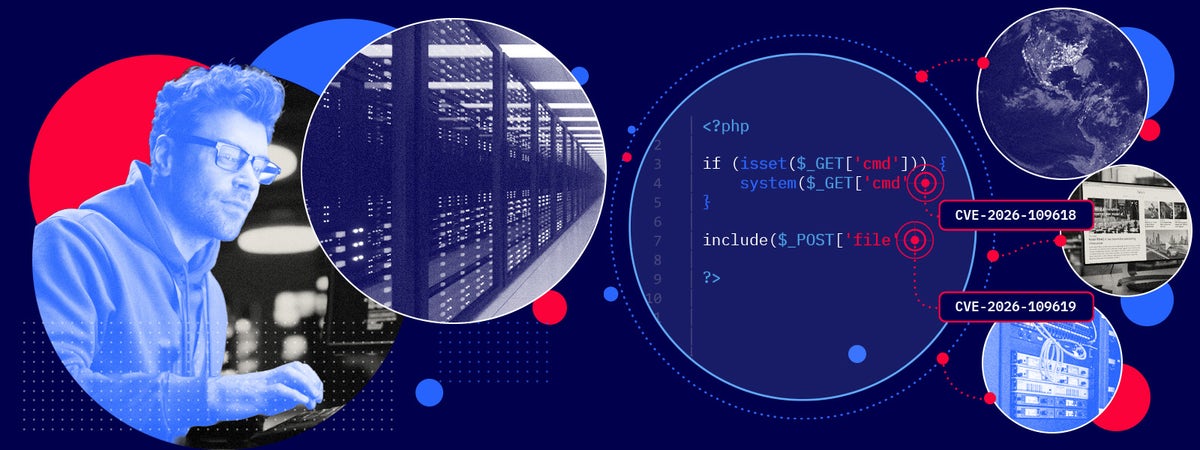
Two critical remote code execution vulnerabilities in the PHP engine, CVE-2026-109618 and CVE-2026-109619 (nicknamed “PHP2Shell”), are reportedly being targeted in active exploitation attempts following the leak of technical details ahead of PHP’s October 21, 2026, security release. Because the flaws affect PHP itself rather than a specific application, websites running vulnerable PHP versions may be exposed, including those built on WordPress, Drupal, and Joomla.
This post covers
0
9
TAG-217 Targets South Korean Financial Services with ARTEX
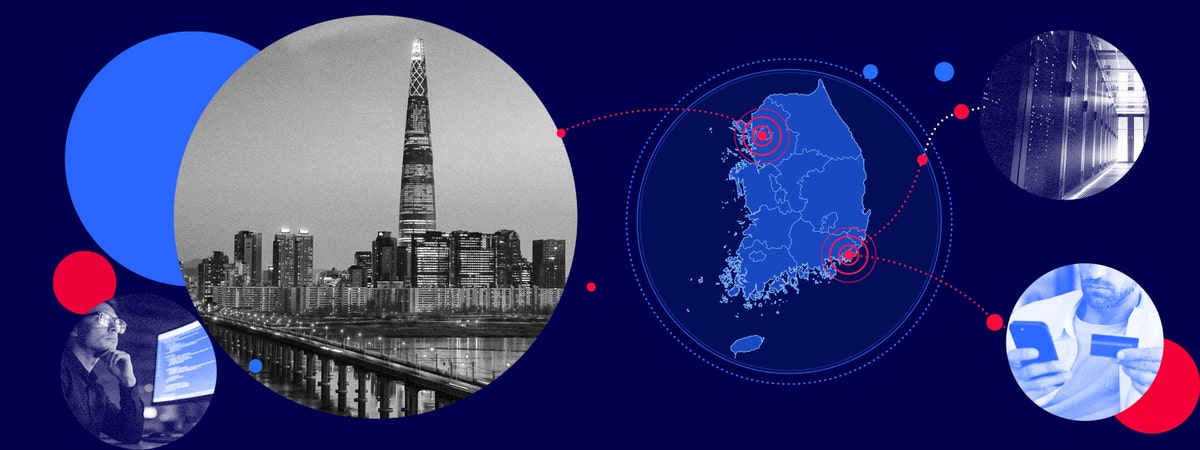
The threat actor linked to recent AI-assisted attacks on South Korean financial institutions was testing infrastructure and assembling attack tools as early as August 2026, weeks before the banking campaign became public, according to new research from Recorded Future’s Insikt Group. Subsequent public reporting indicated that the breaches exposed personal data belonging to at least 68,000 people across at least seven financial institutions.
Insikt Group’s investigation expands the
0
141
Working in Boston at the World’s Largest Intelligence Company
Although Recorded Future was founded by Swedish scientists and innovators, our HQ has always been a key part of the Somerville and Boston tech startup scene. Recognized for our award-winning platform and amazing culture, the team and our HQ have changed quite a bit over the years.
Initially established in Somerville, MA, north of Boston, the Futurists' headquarters was once a laundromat. Twelve years after we set up camp there, it is time for the next chapter. Our HQ has moved to downtow
0
6
Russia Is Tightening Internet Controls, Leading to Operational Risks
Executive Summary
Since mid-2025, the Kremlin has intensified restrictions on digital communications and infrastructure, very likely to suppress the organization of domestic political dissent and conduct digital surveillance within Russia. Increasingly strict measures targeting virtual private networks (VPNs), state-managed internet shutdowns, limitations on civilian communications platforms, and monitoring of domestic and foreign entities very likely represent an escalation from the app
0
9
TAG-193’s Regional Espionage Operations
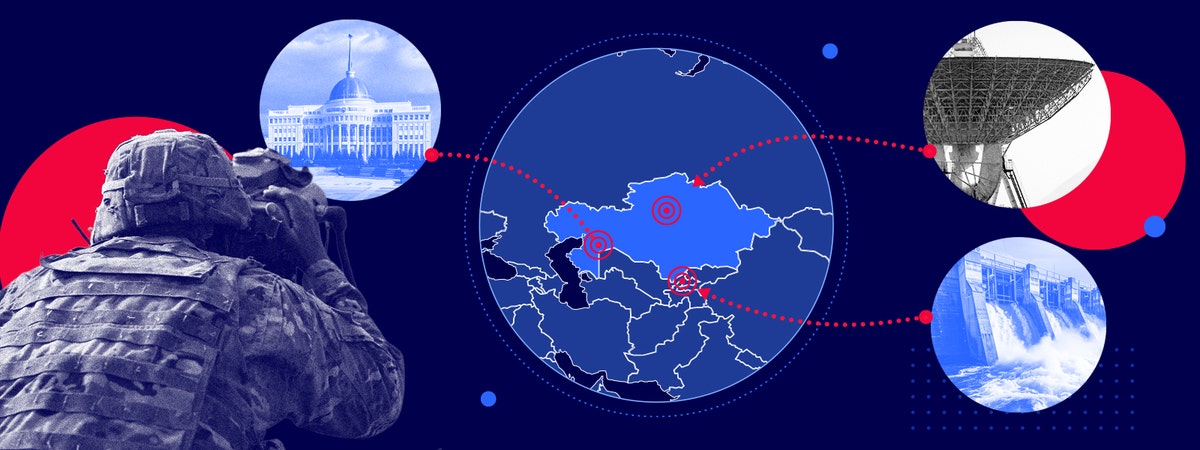
Joint research by Cisco Talos and Recorded Future’s Insikt Group examined sustained cyber-espionage activity by TAG-193 targeting government organizations across Central Asia and the wider Commonwealth of Independent States (CIS). Tracked by Cisco Talos as UAT-6275 and also known as Silent Lynx, TAG-193 combines diplomatic and economic targeting with an interest in environmental policy, water resources, and forestry. Exposed infrastructure provided new visibility into its malware, operational pr
0
8
September 2026 CVE Landscape
In September 2026, Insikt Group® identified 94 high-impact vulnerabilities to prioritize for remediation, 59 of which had a Very Critical Recorded Future Risk Score. This represents a 29% increase from last month. 43 of these vulnerabilities were surfaced through the US Cybersecurity and Infrastructure Security Agency (CISA)’s Known Exploited Vulnerabilities (KEV) catalog, 37 were reported in open sources and validated by Insikt Group, and 14 were exclusively surfaced through honeypot data.
0
8
Malware Indicators of Compromise (IoCs) | Recorded Future
One malware hash can turn a vague alert into a concrete investigation. Analysts can search endpoints for the exact file, trace where it appeared, and determine whether related activity exists elsewhere. But if the attacker changes the file, the hash changes too. Domains and Internet Protocol (IP) addresses can also lose relevance as attackers rotate infrastructure.
This is why malware indicators of compromise work best as evidence within a larger investigation, not as isolated entries on
0
8
Recorded Future Introduces AI Infrastructure Indicator Lists, Strengthening AI Governance
Today, Recorded Future is announcing AI Infrastructure Indicator Lists, curated datasets for security teams to identify, monitor, and implement controls for AI-related network traffic. AI Infrastructure Indicator Lists are included for free for Recorded Future customers with a Cyber Operations license.
Artificial intelligence has increasingly become enterprise infrastructure and organizations are now confronting unsanctioned tool use (also known as shadow AI), data exposure, and autonomo
0
60
Japan Adopts Proactive Cyber Defense Strategy
Executive Summary
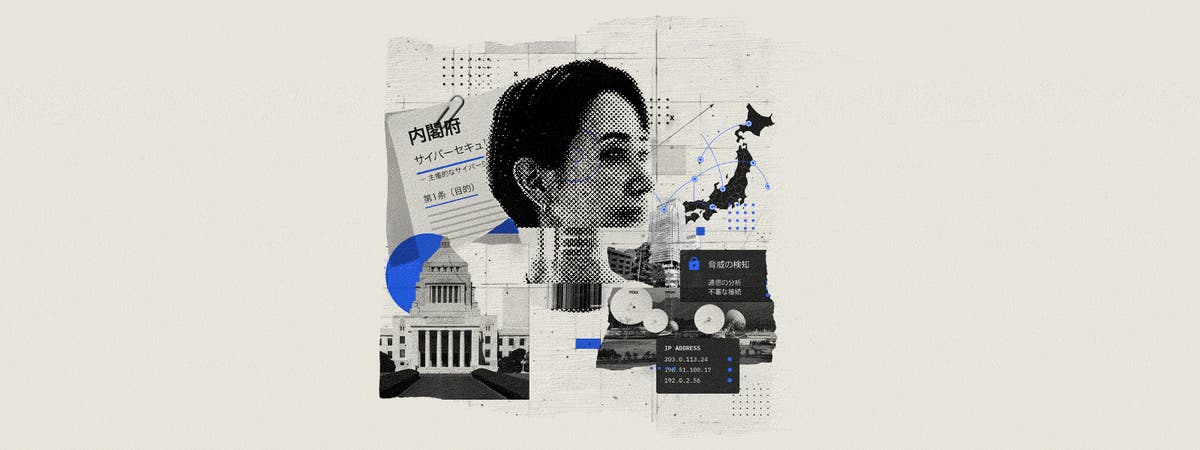
Japan’s Active Cyber Defense (ACD) framework shifts the country from voluntary information sharing and post-incident investigation to mandatory reporting, preventive communications analysis, and limited disruption of attack infrastructure. Beginning October 1, 2026, designated critical infrastructure operators must notify the government about covered systems and report qualifying incidents; those with existing systems have six months to submit initial notifications. New
0
7
Recorded Future Debuts Autonomous Defense, Built for Machine-Speed Threats
Rethinking defense entirely
We know attackers are already using AI to operate at machine speed, running more frequent and more effective attacks. They're automating reconnaissance, standing up infrastructure, and pivoting faster than human analysts can triage an alert. We have seen the cyber kill chain that used to unfold step by step now happens in the blink of an eye, and defenders are struggling to keep up in a fight that no longer gives them time to react.
It's clear that org
0
10
Social Engineering in the Age of Synthetic Media
Most AI-enabled social engineering can still be addressed through existing defenses, but synthetic media attacks require organizations to adapt those defenses and stop treating a familiar face or voice as proof of identity.
Many uses of AI in social engineering, including personalizing phishing messages, building fraudulent websites, and automating responses, make established techniques faster, cheaper, and easier to scale. Although organizations must adapt their defenses to addres
0
14
Recorded Future Launches MCP, the Intelligence Layer for Agentic Security Operations
Recorded Future MCP is now generally available, giving AI agents and LLM workflows direct access to Recorded Future's Intelligence Graph® and enabling precise, trustworthy, and cost-effective decision-making at machine speed and scale.
0
22
Using Threat Intelligence to Stop Ransomware Attacks
Ransomware does not start when files are encrypted. By then, an attacker may already have obtained valid credentials, entered the network, moved between systems and established a command-and-control (C2) channel.
That gives defenders an earlier window to act. Ransomware threat intelligence helps security teams identify the actors, infrastructure and access methods connected to ransomware activity before an attack reaches its final stage. Instead of waiting for an endpoint alert or ransom
0
18
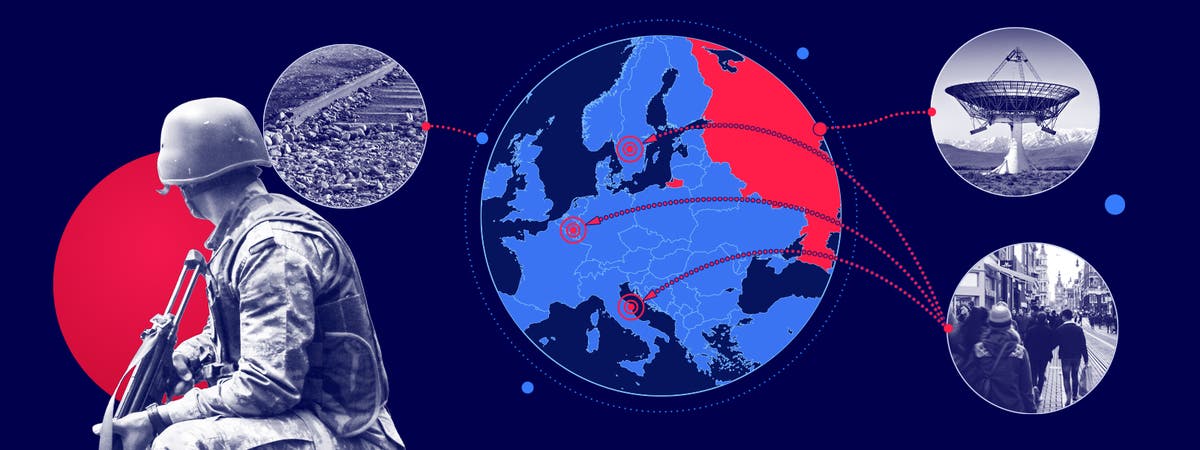
Russia Escalating Hybrid Attacks Across Europe
Since Russia’s full-scale invasion of Ukraine in February 2022, Russia has escalated its use of hybrid, asymmetric warfare across Europe, far beyond the former Soviet Union, where Russia historically focused its aggression. These tactics fall under a Russian military strategy known as New Generation Warfare (NGW). Insikt Group assesses that Russia is likely to escalate NGW tactics over the next two years, potentially culminating in a full-scale NGW campaign. Europe-based private and public secto
0
18
The Lure Isn't The Malware. It's Your Logo.
Recorded Future's Insikt GroupⓇ has been tracking ClickFix, a social engineering technique that turns a familiar logo or verification prompt into the entry point for an attack. Here's what that research reveals about catching it, and why it's now running inside Malicious Site Monitoring, part of our newly launched Digital Risk Protection solution.
Recorded Future's Insikt GroupⓇ, our team of threat intelligence analysts and security researchers, has been tracking a te
0
14
Agent Running in the Age of AI
The intelligence community has always done things the same way: Identify a potential source (a target); make a recruitment (an agent); train, brief, and run the agent in place to collect intelligence of value to decision makers.
A great agent gives the decision maker insight into intent, and a reasoning and decision advantage over his or her adversaries. In some circumstances, this advantage shapes destiny. Control over destiny is commonly called sovereignty.
AI has rapidly made
0
17
Our View on What It Takes To Be Named an Industry-Recognized Threat Intelligence Leader
Recorded Future was just named a Leader in The Forrester Wave™: External Threat Intelligence Service Providers, Q3 2026.
We’re incredibly proud of this acknowledgment, just as we are of every recognition we’ve received over the years. Behind every one of these industry evaluations is a lot of work that readers never see — including product demonstrations, customer reference calls, briefing presentations, and formal questionnaire submissions — all of it condensed into a single final repor
0
9
The New Rules of Machine Speed Defense
Global security frameworks are evolving: Security organizations are increasingly leveraging global frameworks to navigate the complexities of AI-enabled threats, balancing the need for standardized best practices with the necessity of business-specific risk decisions.
Intelligence-led defense is essential: Modern, intelligence-led defense generally requires operationalizing security at machine speed by integrating enriched, contextual threat data, which better enables strategic,
0
14
Prediction Markets Emerge as a New Vertical for Traffer Teams
Executive Summary
Since the spring of 2026, Insikt Group has observed multiple Russian-language traffer teams th
0
7
Behind Japan’s Warnings of a Cyber Crisis
Reporting on cyberattacks against Japanese entities rose 48% between Q2 and Q3 2026, encompassing ransomware, exploitati
0
10
PHP2Shell Exploitation: Two Critical PHP Flaws Explained
Two critical remote code execution vulnerabilities in the PHP engine, CVE-2026-109618 and CVE-2026-109619 (nicknamed “PH
0
9
TAG-217 Targets South Korean Financial Services with ARTEX
The threat actor linked to recent AI-assisted attacks on South Korean financial institutions was testing infrastructure
0
141
Working in Boston at the World’s Largest Intelligence Company
Although Recorded Future was founded by Swedish scientists and innovators, our HQ has always been a key part of the Some
0
6
Russia Is Tightening Internet Controls, Leading to Operational Risks
Executive Summary
Since mid-2025, the Kremlin has intensified restrictions on digital communications and infrast
0
9
TAG-193’s Regional Espionage Operations
Joint research by Cisco Talos and Recorded Future’s Insikt Group examined sustained cyber-espionage activity by TAG-193
0
8
September 2026 CVE Landscape
In September 2026, Insikt Group® identified 94 high-impact vulnerabilities to prioritize for remediation, 59 of which ha
0
8
Malware Indicators of Compromise (IoCs) | Recorded Future
One malware hash can turn a vague alert into a concrete investigation. Analysts can search endpoints for the exact file,
0
8
Recorded Future Introduces AI Infrastructure Indicator Lists, Strengthening AI Governance
Today, Recorded Future is announcing AI Infrastructure Indicator Lists, curated datasets for security teams to identify,
0
60
Japan Adopts Proactive Cyber Defense Strategy
Executive Summary
Japan’s Active Cyber Defense (ACD) framework shifts the country from voluntary information sha
0
7
Recorded Future Debuts Autonomous Defense, Built for Machine-Speed Threats
Rethinking defense entirely
We know attackers are already using AI to operate at machine speed, running more fre
0
10
Social Engineering in the Age of Synthetic Media
Most AI-enabled social engineering can still be addressed through existing defenses, but synthetic media attacks require
0
14
Recorded Future Launches MCP, the Intelligence Layer for Agentic Security Operations
Recorded Future MCP is now generally available, giving AI agents and LLM workflows direct access to Recorded Future's In
0
22
Using Threat Intelligence to Stop Ransomware Attacks
Ransomware does not start when files are encrypted. By then, an attacker may already have obtained valid credentials, en
0
18
Russia Escalating Hybrid Attacks Across Europe
Since Russia’s full-scale invasion of Ukraine in February 2022, Russia has escalated its use of hybrid, asymmetric warfa
0
18
The Lure Isn't The Malware. It's Your Logo.
Recorded Future's Insikt GroupⓇ has been tracking ClickFix, a social engineering technique that turns a familiar logo or
0
14
Agent Running in the Age of AI
The intelligence community has always done things the same way: Identify a potential source (a target); make a recruitme
0
17
Prediction Markets Emerge as a New Vertical for Traffer Teams
Executive Summary
Since the spring of 2026, Insikt Group has observed multiple Russian-language traffer teams that have qu…
💬 0
👁 7
Behind Japan’s Warnings of a Cyber Crisis
Recorded Future · Oct 22, 2026
💬 0
👁 10
PHP2Shell Exploitation: Two Critical PHP Flaws Explained
Recorded Future · Oct 21, 2026
💬 0
👁 9
TAG-217 Targets South Korean Financial Services with ARTEX
Recorded Future · Oct 16, 2026
💬 0
👁 141

Working in Boston at the World’s Largest Intelligence Company
Recorded Future · Oct 15, 2026

Russia Is Tightening Internet Controls, Leading to Operational Risks
Recorded Future · Oct 15, 2026

TAG-193’s Regional Espionage Operations
Recorded Future · Oct 14, 2026

September 2026 CVE Landscape
Recorded Future · Oct 13, 2026
Malware Indicators of Compromise (IoCs) | Recorded Future
One malware hash can turn a vague alert into a concrete investigation. Analysts can search endpoints for the exact file, trace whe…
💬 0
👁 8
Recorded Future Introduces AI Infrastructure Indicator Lists, Strengthening AI Governance
Recorded Future · Oct 9, 2026
💬 0
👁 60
Japan Adopts Proactive Cyber Defense Strategy
Recorded Future · Oct 8, 2026
💬 0
👁 7
Recorded Future Debuts Autonomous Defense, Built for Machine-Speed Threats
Recorded Future · Sep 30, 2026
💬 0
👁 10

Social Engineering in the Age of Synthetic Media
Recorded Future · Sep 29, 2026

Recorded Future Launches MCP, the Intelligence Layer for Agentic Security Operations
Recorded Future · Sep 28, 2026

Using Threat Intelligence to Stop Ransomware Attacks
Recorded Future · Sep 25, 2026

Russia Escalating Hybrid Attacks Across Europe
Recorded Future · Sep 24, 2026
The Lure Isn't The Malware. It's Your Logo.
Recorded Future's Insikt GroupⓇ has been tracking ClickFix, a social engineering technique that turns a familiar logo or verificat…
💬 0
👁 14
Agent Running in the Age of AI
Recorded Future · Sep 22, 2026
💬 0
👁 17
Our View on What It Takes To Be Named an Industry-Recognized Threat Intelligence Leader
Recorded Future · Sep 17, 2026
💬 0
👁 9
The New Rules of Machine Speed Defense
Recorded Future · Sep 17, 2026
💬 0
👁 14
Prediction Markets Emerge as a New Vertical for Traffer Teams
Executive Summary
Since the spring of 2026, Insikt Group has observed multiple Russian-language traffer teams that have quickly adapted affiliate-fraud models to capitalize on growing public interest in prediction markets such as PolyMarket and Kalshi. The platforms offered by three such teams — AtlasCore, PolyFucked, and Magnetic Team — provide websites, administrative panels, cryptocurrency payment infrastructure, victim-management capabilities, technical support, and promotional guida
0
7 👁
Behind Japan’s Warnings of a Cyber Crisis
Reporting on cyberattacks against Japanese entities rose 48% between Q2 and Q3 2026, encompassing ransomware, exploitation of vulnerabilities, credential leaks, and service disruptions. Significant incidents exposed millions of customer records and disrupted operations across multiple sectors, with attacks on shared service providers extending the impact to downstream organizations. Further incidents in October 2026 indicate that these trends have persisted into Q4. This report examines potentia
0
10 👁
PHP2Shell Exploitation: Two Critical PHP Flaws Explained
Two critical remote code execution vulnerabilities in the PHP engine, CVE-2026-109618 and CVE-2026-109619 (nicknamed “PHP2Shell”), are reportedly being targeted in active exploitation attempts following the leak of technical details ahead of PHP’s October 21, 2026, security release. Because the flaws affect PHP itself rather than a specific application, websites running vulnerable PHP versions may be exposed, including those built on WordPress, Drupal, and Joomla.
This post covers
0
9 👁
TAG-217 Targets South Korean Financial Services with ARTEX
The threat actor linked to recent AI-assisted attacks on South Korean financial institutions was testing infrastructure and assembling attack tools as early as August 2026, weeks before the banking campaign became public, according to new research from Recorded Future’s Insikt Group. Subsequent public reporting indicated that the breaches exposed personal data belonging to at least 68,000 people across at least seven financial institutions.
Insikt Group’s investigation expands the
0
141 👁
Working in Boston at the World’s Largest Intelligence Company
Although Recorded Future was founded by Swedish scientists and innovators, our HQ has always been a key part of the Somerville and Boston tech startup scene. Recognized for our award-winning platform and amazing culture, the team and our HQ have changed quite a bit over the years.
Initially established in Somerville, MA, north of Boston, the Futurists' headquarters was once a laundromat. Twelve years after we set up camp there, it is time for the next chapter. Our HQ has moved to downtow
0
6 👁
Russia Is Tightening Internet Controls, Leading to Operational Risks
Executive Summary
Since mid-2025, the Kremlin has intensified restrictions on digital communications and infrastructure, very likely to suppress the organization of domestic political dissent and conduct digital surveillance within Russia. Increasingly strict measures targeting virtual private networks (VPNs), state-managed internet shutdowns, limitations on civilian communications platforms, and monitoring of domestic and foreign entities very likely represent an escalation from the app
0
9 👁
TAG-193’s Regional Espionage Operations
Joint research by Cisco Talos and Recorded Future’s Insikt Group examined sustained cyber-espionage activity by TAG-193 targeting government organizations across Central Asia and the wider Commonwealth of Independent States (CIS). Tracked by Cisco Talos as UAT-6275 and also known as Silent Lynx, TAG-193 combines diplomatic and economic targeting with an interest in environmental policy, water resources, and forestry. Exposed infrastructure provided new visibility into its malware, operational pr
0
8 👁
September 2026 CVE Landscape
In September 2026, Insikt Group® identified 94 high-impact vulnerabilities to prioritize for remediation, 59 of which had a Very Critical Recorded Future Risk Score. This represents a 29% increase from last month. 43 of these vulnerabilities were surfaced through the US Cybersecurity and Infrastructure Security Agency (CISA)’s Known Exploited Vulnerabilities (KEV) catalog, 37 were reported in open sources and validated by Insikt Group, and 14 were exclusively surfaced through honeypot data.
0
8 👁
Malware Indicators of Compromise (IoCs) | Recorded Future
One malware hash can turn a vague alert into a concrete investigation. Analysts can search endpoints for the exact file, trace where it appeared, and determine whether related activity exists elsewhere. But if the attacker changes the file, the hash changes too. Domains and Internet Protocol (IP) addresses can also lose relevance as attackers rotate infrastructure.
This is why malware indicators of compromise work best as evidence within a larger investigation, not as isolated entries on
0
8 👁
Recorded Future Introduces AI Infrastructure Indicator Lists, Strengthening AI Governance
Today, Recorded Future is announcing AI Infrastructure Indicator Lists, curated datasets for security teams to identify, monitor, and implement controls for AI-related network traffic. AI Infrastructure Indicator Lists are included for free for Recorded Future customers with a Cyber Operations license.
Artificial intelligence has increasingly become enterprise infrastructure and organizations are now confronting unsanctioned tool use (also known as shadow AI), data exposure, and autonomo
0
60 👁
Japan Adopts Proactive Cyber Defense Strategy
Executive Summary
Japan’s Active Cyber Defense (ACD) framework shifts the country from voluntary information sharing and post-incident investigation to mandatory reporting, preventive communications analysis, and limited disruption of attack infrastructure. Beginning October 1, 2026, designated critical infrastructure operators must notify the government about covered systems and report qualifying incidents; those with existing systems have six months to submit initial notifications. New
0
7 👁
Recorded Future Debuts Autonomous Defense, Built for Machine-Speed Threats
Rethinking defense entirely
We know attackers are already using AI to operate at machine speed, running more frequent and more effective attacks. They're automating reconnaissance, standing up infrastructure, and pivoting faster than human analysts can triage an alert. We have seen the cyber kill chain that used to unfold step by step now happens in the blink of an eye, and defenders are struggling to keep up in a fight that no longer gives them time to react.
It's clear that org
0
10 👁
Social Engineering in the Age of Synthetic Media
Most AI-enabled social engineering can still be addressed through existing defenses, but synthetic media attacks require organizations to adapt those defenses and stop treating a familiar face or voice as proof of identity.
Many uses of AI in social engineering, including personalizing phishing messages, building fraudulent websites, and automating responses, make established techniques faster, cheaper, and easier to scale. Although organizations must adapt their defenses to addres
0
14 👁
Recorded Future Launches MCP, the Intelligence Layer for Agentic Security Operations
Recorded Future MCP is now generally available, giving AI agents and LLM workflows direct access to Recorded Future's Intelligence Graph® and enabling precise, trustworthy, and cost-effective decision-making at machine speed and scale.
0
22 👁
Using Threat Intelligence to Stop Ransomware Attacks
Ransomware does not start when files are encrypted. By then, an attacker may already have obtained valid credentials, entered the network, moved between systems and established a command-and-control (C2) channel.
That gives defenders an earlier window to act. Ransomware threat intelligence helps security teams identify the actors, infrastructure and access methods connected to ransomware activity before an attack reaches its final stage. Instead of waiting for an endpoint alert or ransom
0
18 👁
Russia Escalating Hybrid Attacks Across Europe
Since Russia’s full-scale invasion of Ukraine in February 2022, Russia has escalated its use of hybrid, asymmetric warfare across Europe, far beyond the former Soviet Union, where Russia historically focused its aggression. These tactics fall under a Russian military strategy known as New Generation Warfare (NGW). Insikt Group assesses that Russia is likely to escalate NGW tactics over the next two years, potentially culminating in a full-scale NGW campaign. Europe-based private and public secto
0
18 👁
The Lure Isn't The Malware. It's Your Logo.
Recorded Future's Insikt GroupⓇ has been tracking ClickFix, a social engineering technique that turns a familiar logo or verification prompt into the entry point for an attack. Here's what that research reveals about catching it, and why it's now running inside Malicious Site Monitoring, part of our newly launched Digital Risk Protection solution.
Recorded Future's Insikt GroupⓇ, our team of threat intelligence analysts and security researchers, has been tracking a te
0
14 👁
Agent Running in the Age of AI
The intelligence community has always done things the same way: Identify a potential source (a target); make a recruitment (an agent); train, brief, and run the agent in place to collect intelligence of value to decision makers.
A great agent gives the decision maker insight into intent, and a reasoning and decision advantage over his or her adversaries. In some circumstances, this advantage shapes destiny. Control over destiny is commonly called sovereignty.
AI has rapidly made
0
17 👁
Our View on What It Takes To Be Named an Industry-Recognized Threat Intelligence Leader
Recorded Future was just named a Leader in The Forrester Wave™: External Threat Intelligence Service Providers, Q3 2026.
We’re incredibly proud of this acknowledgment, just as we are of every recognition we’ve received over the years. Behind every one of these industry evaluations is a lot of work that readers never see — including product demonstrations, customer reference calls, briefing presentations, and formal questionnaire submissions — all of it condensed into a single final repor
0
9 👁
The New Rules of Machine Speed Defense
Global security frameworks are evolving: Security organizations are increasingly leveraging global frameworks to navigate the complexities of AI-enabled threats, balancing the need for standardized best practices with the necessity of business-specific risk decisions.
Intelligence-led defense is essential: Modern, intelligence-led defense generally requires operationalizing security at machine speed by integrating enriched, contextual threat data, which better enables strategic,
0
14 👁